Azyrion IT AGENTIC CYBER DEFENSE

The right handyour SIEM never had.

Azyrion analyzes the alerts. The decisions stay yours.

A system of specialized AI agents that analyzes every alert autonomously and produces an operational report in minutes, ready for your team.

Stay updated

Get the overview

reCAPTCHA not configured — set RECAPTCHA_SITE_KEY in .env.

SOC automation platform based on specialized AI agents: it doesn't replace the team, it multiplies its operational capacity.

The problem

The SOC is under pressure

Three challenges every SOC leader knows well

Source: cybersecurity industry benchmarks.

Azyrion does not replace the team.

It automates the most time-consuming phase of the alert lifecycle.

How it works

From alert to report, along a pipeline that doesn't improvise

Azyrion receives the alert from your SIEM and hands it to a structured sequence of AI agents. Every phase is tracked, every step has an owner, no alert falls through the cracks.

Alert intake

Azyrion receives a security alert from the SIEM platform.

The agents analyze autonomously

The specialized agents run a sequenced analysis that wraps up in minutes.

An operational report is produced

Once the analysis sequence completes, a ready-to-read report is generated, PDF included.

The agents

The AI agents working alongside your Blue Team

Each one is configurable: system prompt, personality, AI provider, model, and enabled tools.

Network Security Analyst

  • Detects DDoS, port scans, and lateral movement
  • Backs every finding with quantitative metrics: volumes, frequencies, protocols
  • Tools: SIEM queries, IP lookup, event correlator

Incident Responder

  • Digs deep into the evidence and correlates multiple events
  • Identifies the kill chain
  • Produces a remediation plan with prioritized actions

Threat Intelligence Analyst

  • Enriches IPs, domains, and hashes with threat feed data
  • Maps the activity onto the MITRE ATT&CK framework
  • Assesses attacker sophistication: opportunistic, targeted, APT

Compliance & Reporting Analyst

  • Synthesizes everything into a single document
  • Action plan structured across 1h, 4h, 24h, and 7 days
  • Written to be understood even by non-technical readers

Air-gapped ready

The whole solution can run fully air-gapped

Agents, AI models, knowledge base and reports all run inside your own infrastructure. No connection to the outside world is required: no cloud calls, no data sent to third parties.

  • Local AI modelsThe agents run on models installed in-house. No external AI provider is involved.
  • Zero outbound connectionsAnalysis, triage and report generation need no internet access and no calls to vendor services.
  • Data stays in your perimeterAlerts, evidence, knowledge base and PDF reports never leave your network.
  • Your choice, not a constraintAir-gapped is a deployment option: if you prefer, you can still connect an external AI provider.

The dashboard

Every alert has a story. Here's where you find it.

Complete history with a step-by-step breakdown, stats by source and severity, and pipeline success rate. When the agent wraps up, the analyst gets everything already documented.
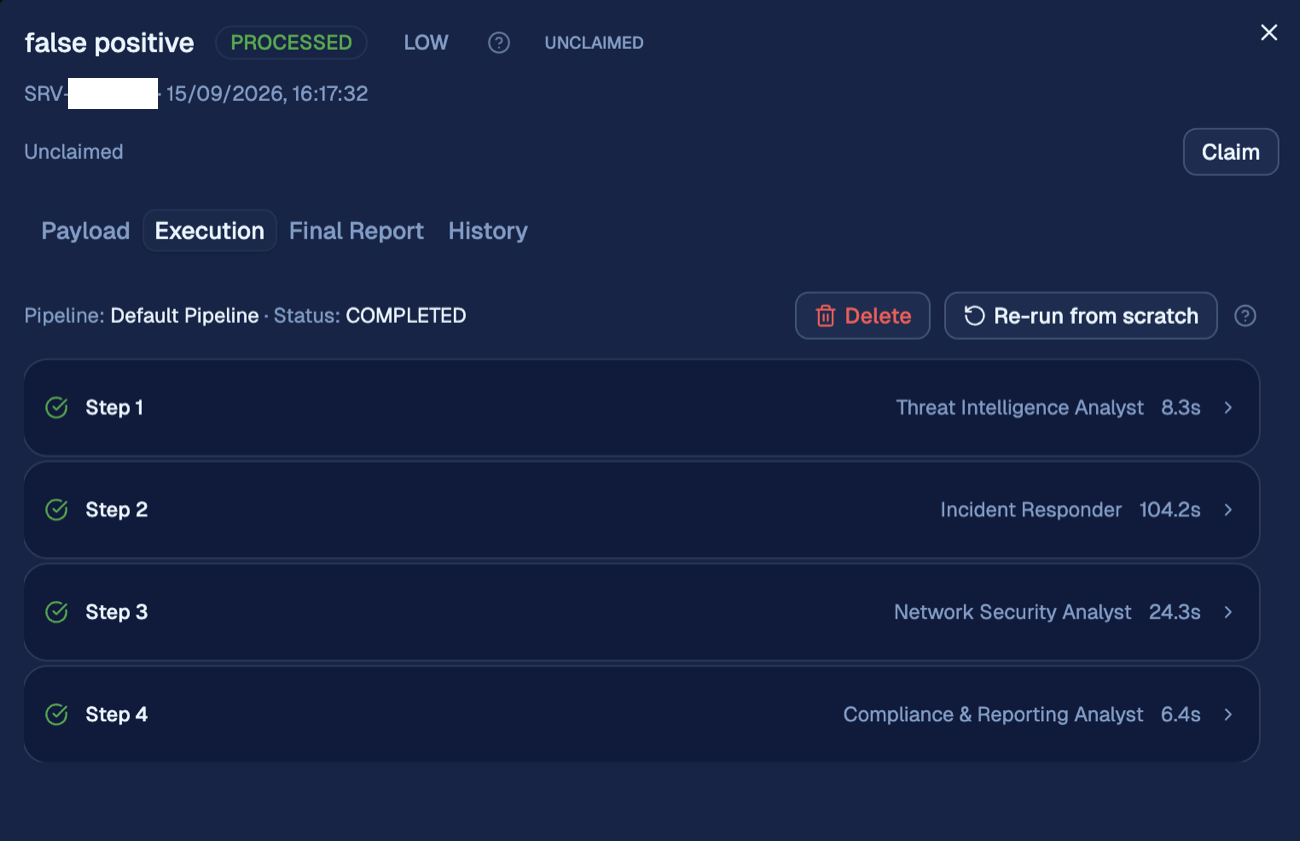
Azyrion dashboard interface: alert detail showing the four-agent pipeline

Demo

See Azyrion in action

A focused, thirty-minute walkthrough of the product.

Try it now

Results

What changes, in practice

Azyrion gives your team concrete support, helping secure the business and cutting down alert fatigue. Figures below are from Azyrion's demo environment.

<4 minutes

average time from alert to complete report

Source: Standard pipeline

100%

alerts tracked with a step-by-step history

Source: All pipelines

0

alerts lost to missing retries or timeouts

Source: Period to be confirmed

Comparison

Azyrion vs. Competitor

Azyrion vs. Competitor
Feature Azyrion Competitor
AI agents configurable with prompts and rules functional, predefined, not configurable
Document RAG integrated company knowledge base none
SIEM compatibility multi-SIEM, vendor-independent tied to its own SIEM
AI provider multi-provider, maximum flexibility proprietary provider, zero flexibility
Air-gapped offline mode available not available
Audit trail deterministic pipeline, full traceability partial or absent
Customization configurable agents and RAG none
Automation adaptive, context-aware AI agents predefined, rigid rules
Cost & complexity optimized for SMBs high

Azyrion

Competitor

AI agents

configurable with prompts and rules
functional, predefined, not configurable

Document RAG

integrated company knowledge base
none

SIEM compatibility

multi-SIEM, vendor-independent
tied to its own SIEM

AI provider

multi-provider, maximum flexibility
proprietary provider, zero flexibility

Air-gapped

offline mode available
not available

Audit trail

deterministic pipeline, full traceability
partial or absent

Customization

configurable agents and RAG
none

Automation

adaptive, context-aware AI agents
predefined, rigid rules

Cost & complexity

optimized for SMBs
high

Frequently asked questions

Still have questions? Check here

Question 01
What is Azyrion?
Azyrion is a team of specialized AI agents that works alongside your security team. When an alert comes in, the agents analyze it, dig deeper and produce a clear report with recommended actions. Your analysts start from the conclusions, not from scratch.
Question 02
What problem does it solve for my company?
Security teams receive hundreds of alerts every day, and many are false alarms. Azyrion does the first round of analysis on all of them, so people can spend their time on real threats. The result: faster responses, less stress and less risk that an important alert goes unnoticed.
Question 03
Does Azyrion replace my security analysts?
No, it empowers them. Azyrion prepares the analysis and suggests what to do, but it does not carry out corrective actions on its own. The final decision always rests with a person, and you keep full control.
Question 04
How much time does it save me?
The time for the first analysis of an alert goes from tens of minutes to a few moments, and the work runs 24 hours a day. The savings depend on the volume of alerts you handle: during evaluation we can measure it together on your real data.
Question 05
Do I have to change the tools I use today?
No. Azyrion connects to the monitoring systems you already use, such as Graylog, Elasticsearch/OpenSearch and Wazuh. There is nothing to replace and no processes to redo. It fits into what you already have.

Still have questions?

Didn't find the answer you were looking for? Get in touch and we'll get back to you within one business day.
Contact us
Azyrion

Request a demo

Ready to get started?

A focused, thirty-minute walkthrough of Azyrion. We'll get back to you within one business day.

Please enter your name.
Please enter a valid work email address.
Please enter your company name.
Please let us know what you'd like to walk through.
Please accept the privacy policy to continue.

reCAPTCHA not configured — set RECAPTCHA_SITE_KEY in .env.

This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.

Not ready for a call yet? Leave your email and we'll send you an overview.

Please enter a valid email address.
Please accept the privacy policy to continue.

reCAPTCHA not configured — set RECAPTCHA_SITE_KEY in .env.

This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.